Application security consultancy
Security testing with a clear path to the fix.
We help B2B software teams assess web apps and APIs, prioritize what to fix, and verify remediation against an agreed scope.

Engagements
Start with the decision you need to make.
Whether it is a release, a customer request, or a recurring review, we agree what to assess and what your team will receive before work starts.
-
Focused review
One application or API with a well-defined release, risk, or customer deadline.
-
Web app & API assessment
A connected review for a SaaS product with several roles, workflows, or supporting endpoints.
-
Recurring assurance
A planned series of reviews around major releases, customer commitments, or remediation milestones.
Reporting and evidence
See what an assessment can tell you.
These fictional examples use the actual Pentester workbench and synthetic data.
-
Multi-tenant SaaS
Follow the same issue from report to retest
A workspace release changes account boundaries. The follow-up distinguishes sample findings that are fixed, still present, or inconclusive when a test account is unavailable.
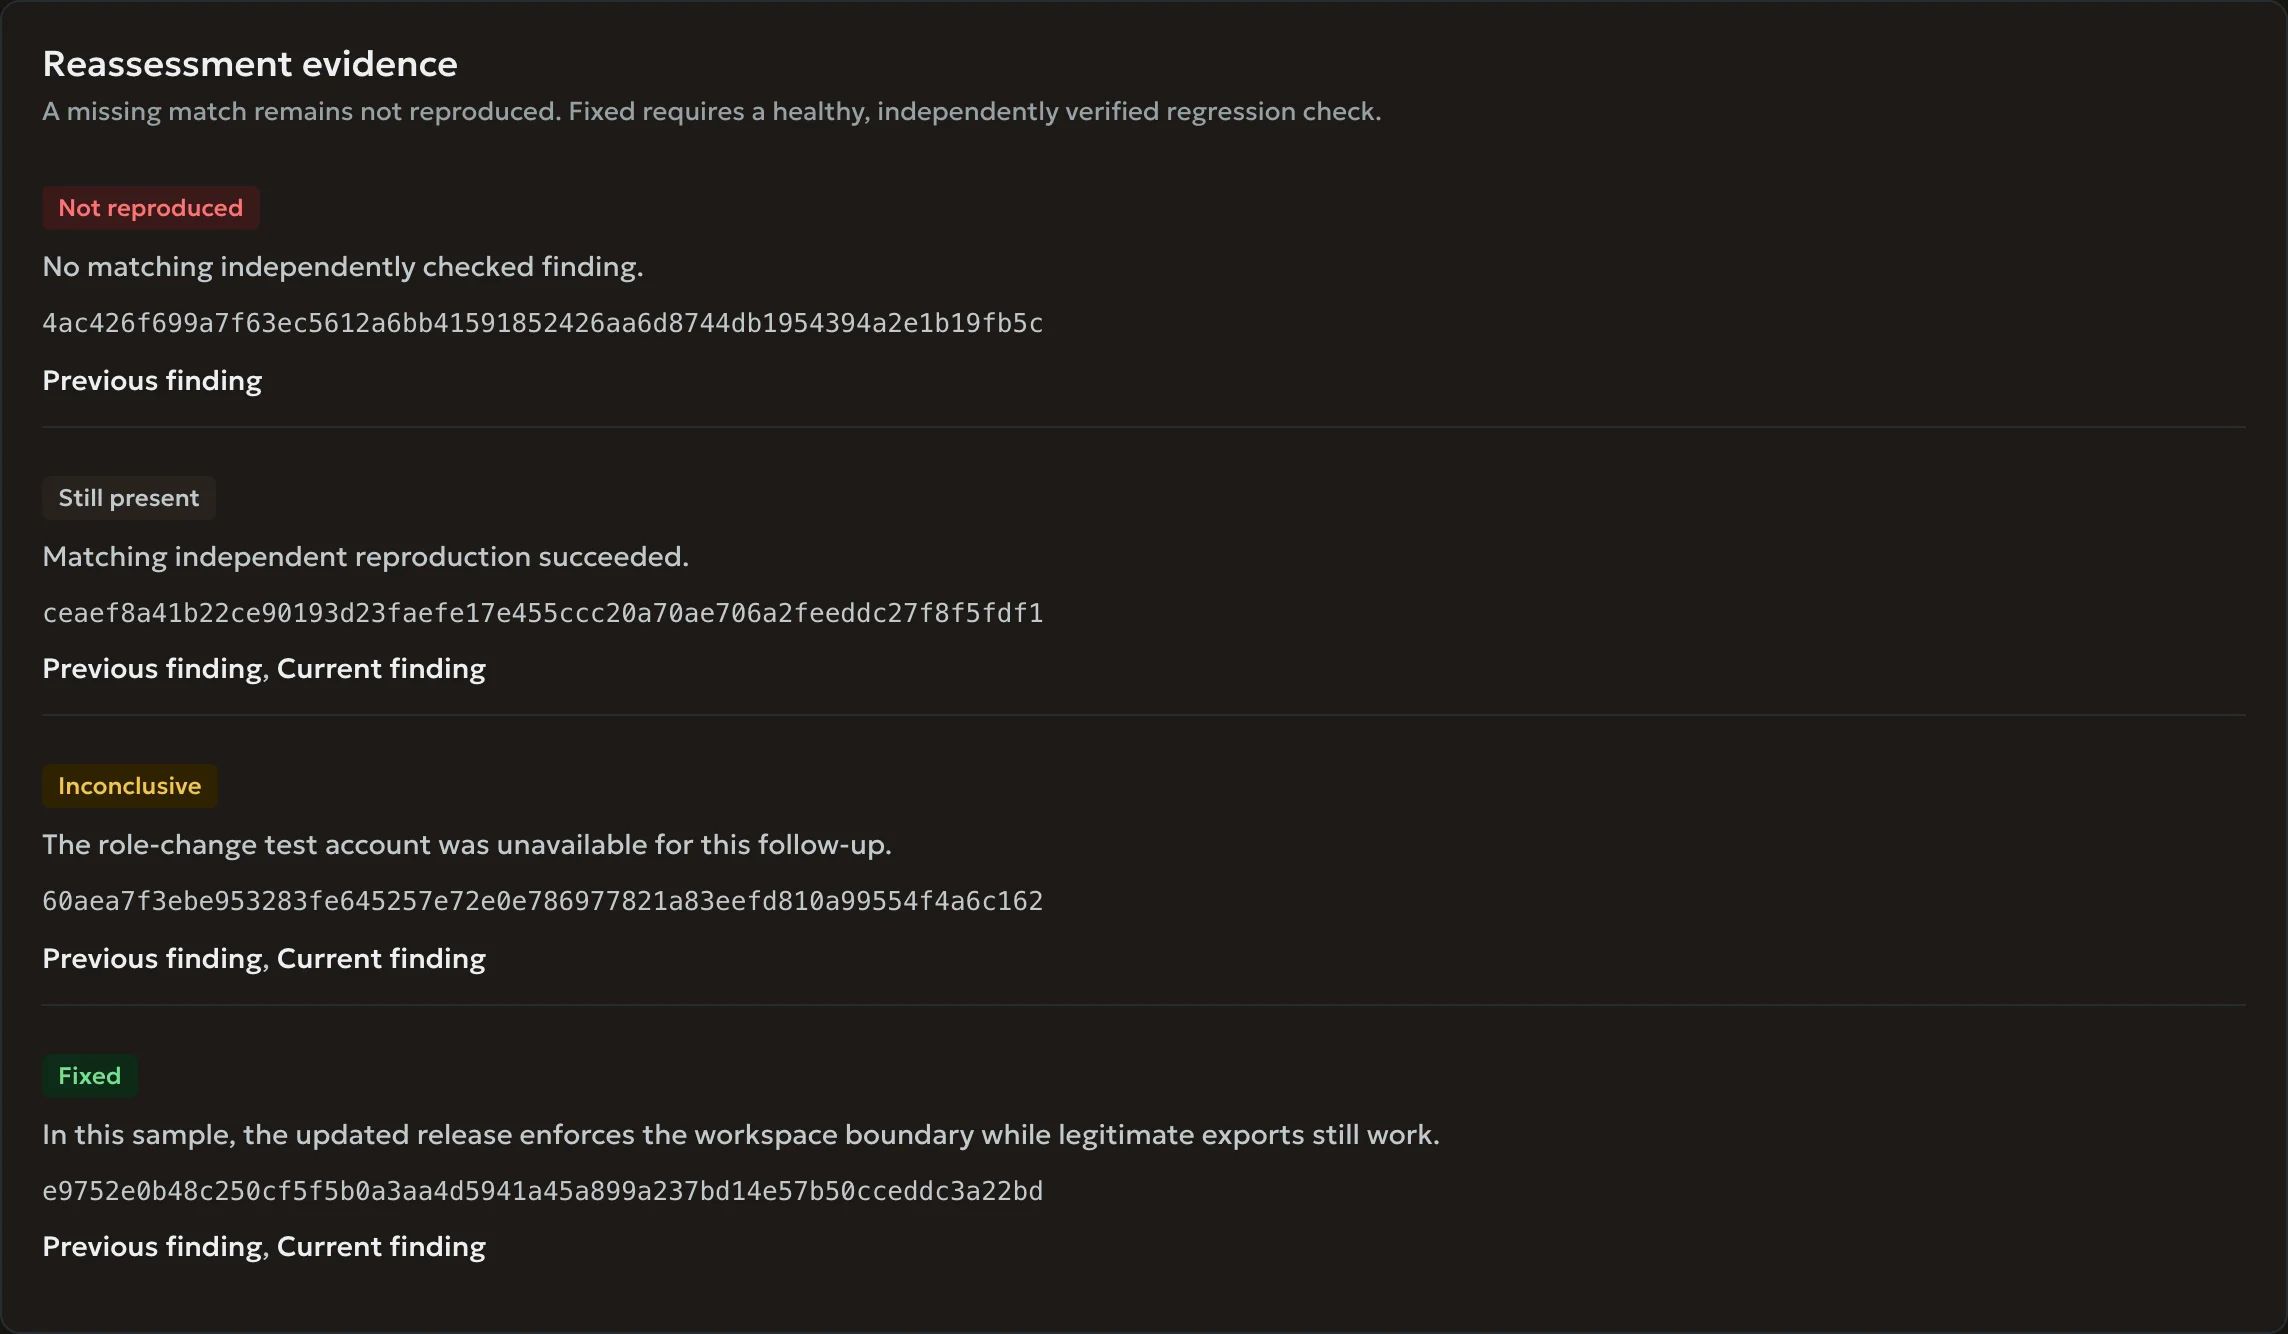
Synthetic data in the Pentester workbench. Open full capture in a new tab -
Billing API and partner access
Give engineering a clear order of work
A billing assessment brings partner permissions, key rotation, and audit coverage into one review. Severity, verification, and review decisions remain separate.
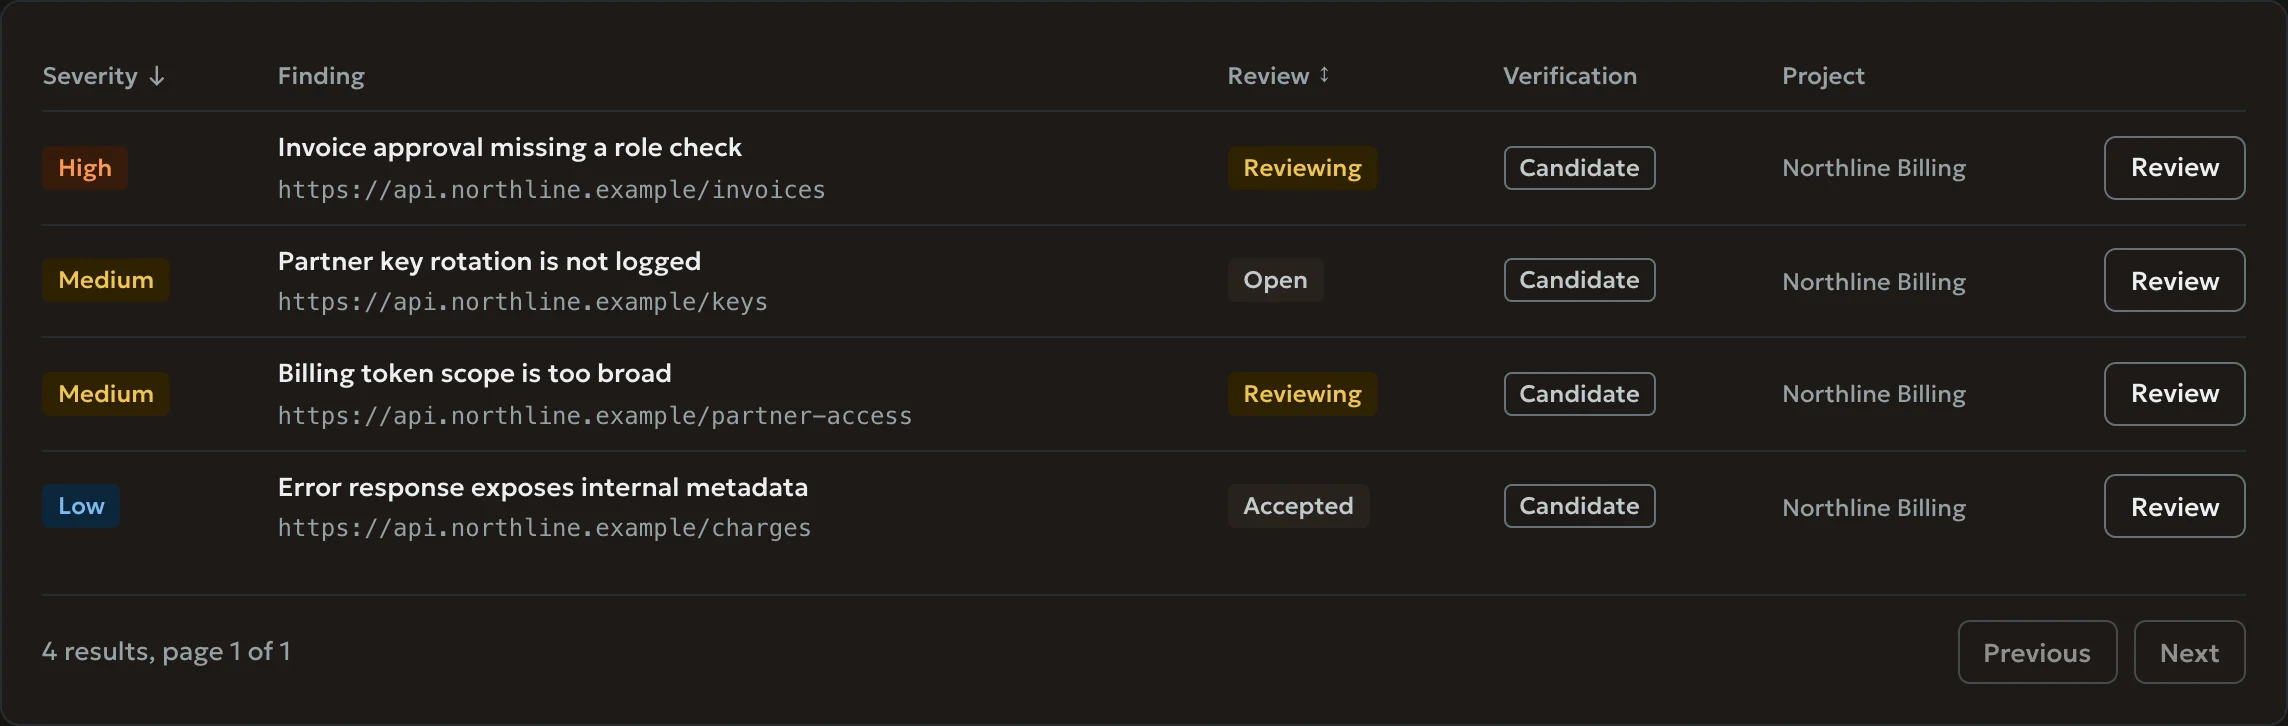
Synthetic data in the Pentester workbench. Open full capture in a new tab -
Source-assisted release review
Hand off evidence with the report
A repository and staging API share one assessment record. The report explains coverage, exclusions, and recommended fixes before a release decision.
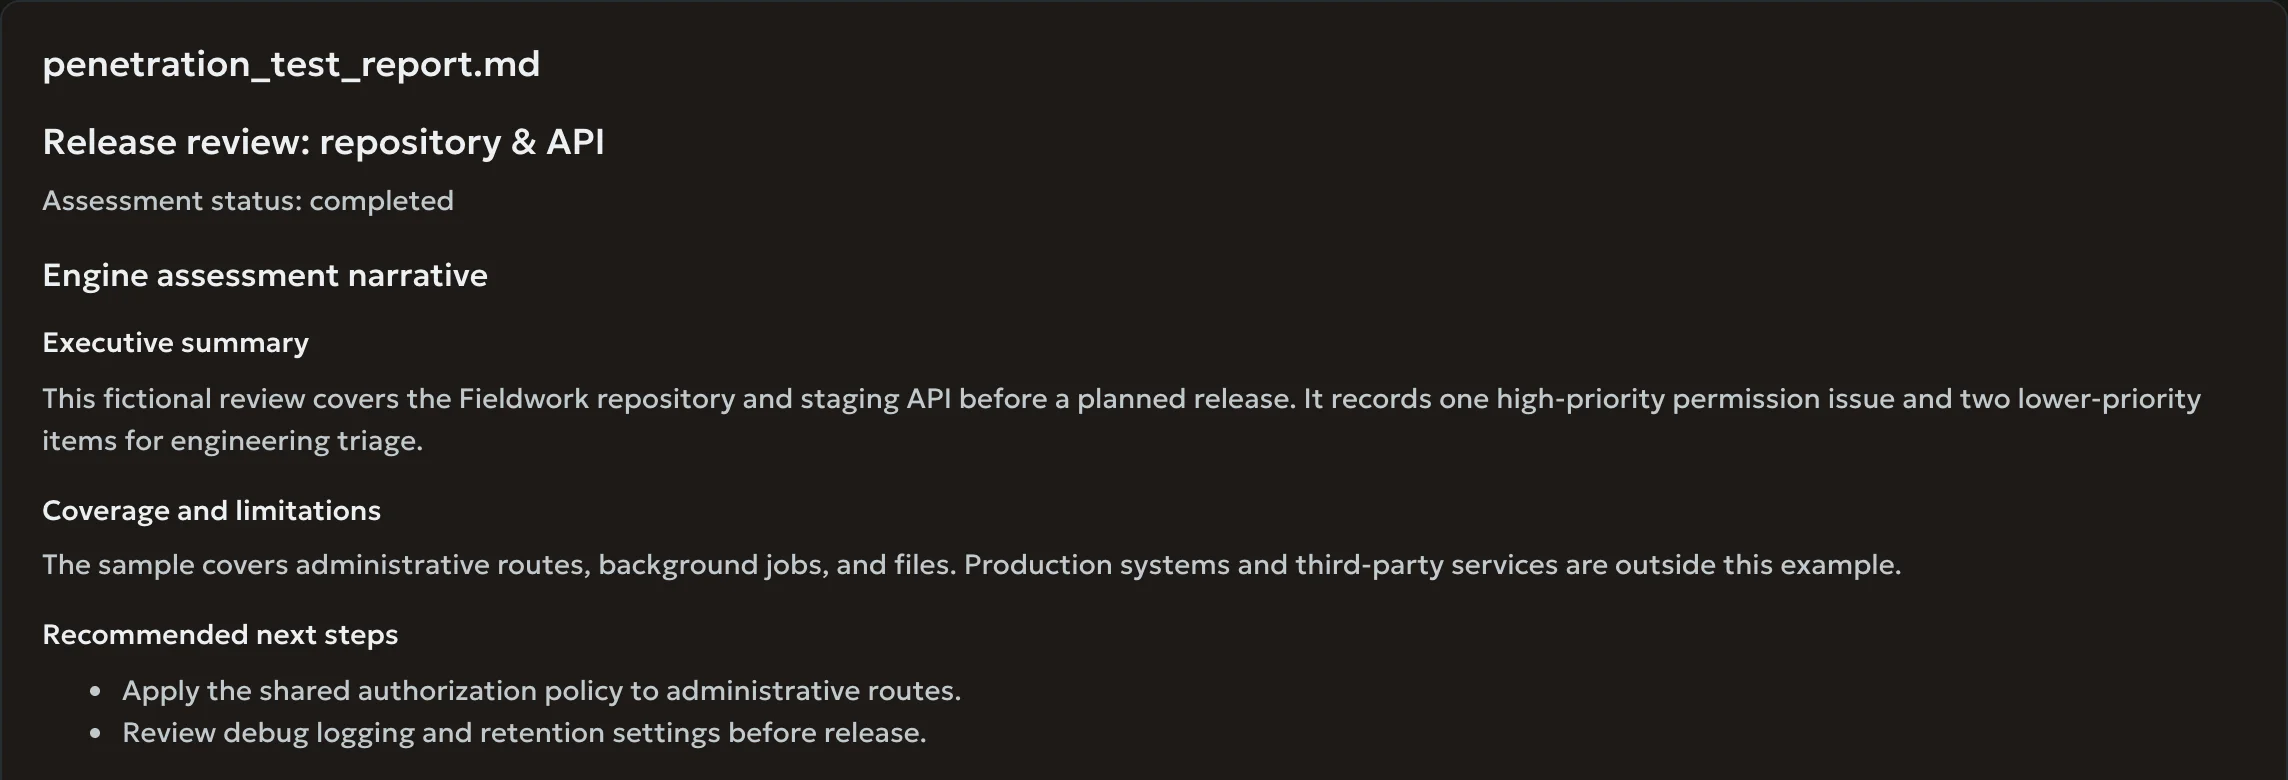
Synthetic data in the Pentester workbench. Open full capture in a new tab


Deliverables
One report for the decision. Evidence for the work.
Use the same record to brief leadership, assign fixes, and prepare for a follow-up.
See our approach- Executive brief
- Summarize what matters to the business, including unresolved risks and limits in coverage.
- Engineering findings
- Document affected surfaces, evidence, impact, and recommended remediation.
- Follow-up record
- Show what changed on retest and what still needs attention, when included in the scope.
Common engagement questions
All frequently asked questionsWhat do you need from our team to get started?
Start with a short description of the product, what you want assessed, and your deadline. Before work begins, we agree on approved assets, access, a testing window, and written authorization.
See the client preparation guideHow is an engagement priced?
CloudGuys sends a fixed quote after agreeing on scope. The price reflects the number of assets, the complexity of the roles and workflows, access, timing, and the follow-up included.
Compare engagement optionsIs a retest included?
The proposal states whether retesting is included, which findings it covers, and when it can be scheduled. A focused retest verifies agreed fixes within the follow-up scope.
See how retest scope is decidedWhat are you preparing for?
Tell us about the product, the deadline, and the systems you want assessed.